In today’s rapidly evolving technological landscape, integrating security measures into the development and operations processes has become paramount. Enter DevSecOps, a methodology that blends development, security, and operations seamlessly into the software development lifecycle (SDLC). As industries grapple with emerging cyber threats and vulnerabilities, DevSecOps emerges as a proactive approach to addressing security concerns right from the outset. This article aims to explain DevSecOps, from its definition, and present best practices tailored for the tech industry.
Defining DevSecOps
DevSecOps, a portmanteau of Development, Security, and Operations, is a collaborative methodology that advocates for integrating security practices within every phase of the software development lifecycle. Unlike traditional approaches, where security is treated as an afterthought, DevSecOps emphasises embedding security measures at the core of the development process. By fostering a culture of shared responsibility and continuous feedback loops, DevSecOps aims to mitigate security risks while ensuring the rapid delivery of high-quality software products.
Core Principles of DevSecOps
- Shift Left Mentality: DevSecOps encourages the “shift left” approach, wherein security considerations are incorporated early in the development process, right from the design phase. By addressing security issues at their inception, teams can prevent vulnerabilities from proliferating throughout the development lifecycle.
- Automation: Automation lies at the heart of DevSecOps practices. By automating security checks, code analysis, vulnerability scanning, and compliance assessments, teams can identify and remediate security issues swiftly, thus minimising manual errors and streamlining the deployment pipeline.
- Continuous Integration and Delivery (CI/CD): DevSecOps advocates for the implementation of CI/CD pipelines, facilitating the rapid and iterative delivery of code while ensuring security checks at each stage of the pipeline. This enables teams to detect and rectify security vulnerabilities in real time, fostering a culture of agility and responsiveness.
- Collaboration and Communication: DevSecOps promotes cross-functional collaboration among development, security, and operations teams. By breaking down silos and fostering open communication channels, teams can collectively address security concerns, share knowledge, and iterate upon security practices collaboratively.
- Security as Code: DevSecOps encourages treating security policies, configurations, and compliance requirements as code. By codifying security measures into version-control repositories, teams can enforce security policies consistently across environments, automate compliance checks, and track changes effectively.
Best Practices for Implementing DevSecOps in Tech Industries
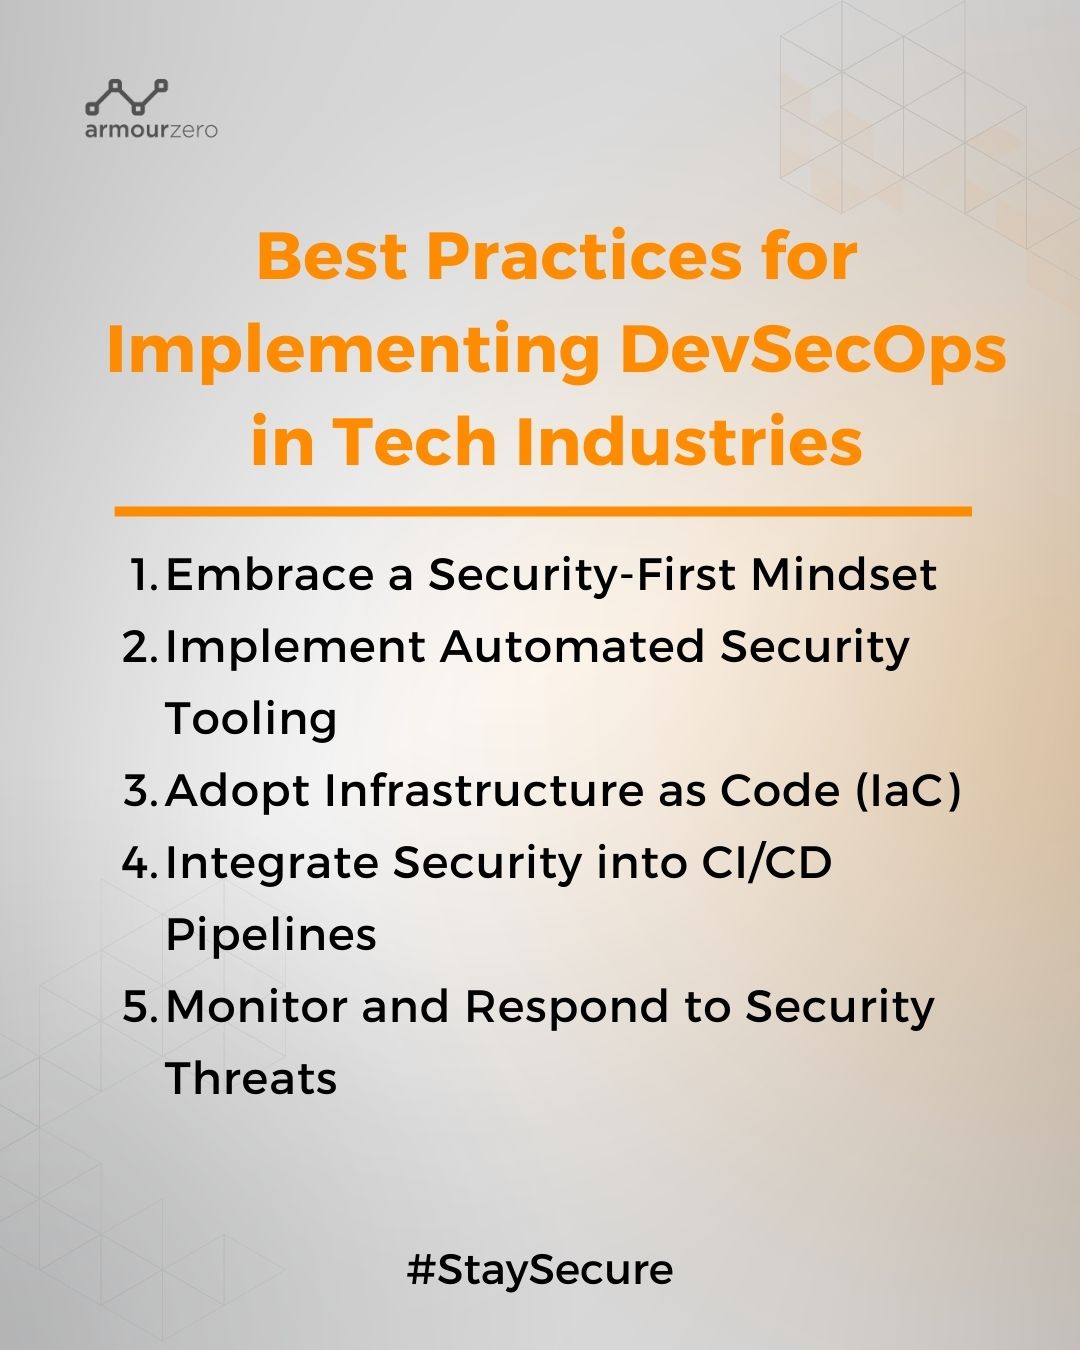
- Embrace a Security-First Mindset: Cultivate a culture where security is prioritised at every stage of the development lifecycle. Encourage developers to undergo security training and promote awareness about common security threats and best practices.
- Implement Automated Security Tooling: Leverage a wide array of automated security tools such as static code analysis, dynamic application security testing (DAST), container scanning, and infrastructure-as-code (IaC) security tools to identify and remediate vulnerabilities early in the development process.
- Adopt Infrastructure as Code (IaC): Embrace IaC principles to programmatically provision and manage infrastructure resources. By codifying infrastructure configurations, security policies, and compliance requirements, teams can ensure consistency, repeatability, and accuracy across environments.
- Integrate Security into CI/CD Pipelines: Embed security checks, such as vulnerability scanning, code analysis, and compliance assessments, into CI/CD pipelines to automate security validations at each stage of the development lifecycle. This enables teams to identify and address security issues proactively, minimising the risk of deploying insecure code into production.
5. Monitor and Respond to Security Threats: Implement robust monitoring and incident response mechanisms to detect and respond to security threats in real time. Leverage security information and event management (SIEM) solutions, intrusion detection systems (IDS), and anomaly detection tools to identify suspicious activities and potential breaches promptly.
Conclusion
In an era marked by escalating cyber threats and stringent regulatory requirements, DevSecOps emerges as a pragmatic approach for fostering secure and resilient software development practices. By integrating security into every facet of the development lifecycle, DevSecOps empowers organisations to proactively mitigate security risks, accelerate time-to-market, and enhance overall software quality. As the tech industry continues to embrace DevSecOps principles, cultivating a culture of collaboration, automation, and continuous improvement will be pivotal in navigating the complexities of modern software development securely.
Safeguard Your Source Code and Business
Simplify your DevSecOps with AI-Powered Platform, Start ScoutTwo for Free now!
Written by:
Bernadetta Septarini (Content Marketing). Experienced content marketing and social media in the information technology and services industry.
Share this post
Subscribe
Related Posts
What Is Code Security Assessment?
- 30 Sep 2026
- By:Bernadetta Septarini
- Category: ArmourHacks
Learn what Code Security Assessment is, why continuous assessment matters, and how SAST, SCA, SBOM, IaC and Secret Scanning help reduce application risk.
What Is Web Application Security Analysis?
- 24 Sep 2026
- By:Bernadetta Septarini
- Category: ArmourHacks
Learn what web application security is, why it matters, common vulnerabilities, and how organisations can use DAST and vulnerability management to reduce risk.
What Is Automated Vulnerability Management?
- 17 Sep 2026
- By:Bernadetta Septarini
- Category: ArmourHacks
Automated Vulnerability Management continuously discovers, validates, and remediates vulnerabilities across applications. Learn how AVM strengthens security.
Multi-Cloud Security: Managing Risk Across Cloud Infrastructures
- 26 Aug 2026
- By:Bernadetta Septarini
- Category: ArmourHacks
Discover why multi-cloud security is becoming essential and how continuous security monitoring helps organisations manage risk across multiple cloud environments.